The real question
The hard part isn’t the breach. It’s the question after it.
Breaches happen to careful, decent businesses every week; that part is close to inevitable. What decides how it goes is the question that always follows: “had you taken reasonable steps?” The Privacy Act often asks it. Directors’ duties ask it. Health records laws ask it. The GDPR asks it as “appropriate technical and organisational measures”. The businesses that answer well aren’t lucky; they prepared an answer before they needed one.
And “reasonable” doesn’t mean enterprise-grade. It means proportionate to a business your size, which is exactly what sector guidance, the legal profession’s guides among the first, points to.
Queensland Law Society · Privacy Program Starter Guide (June 2026)
What you’ll see
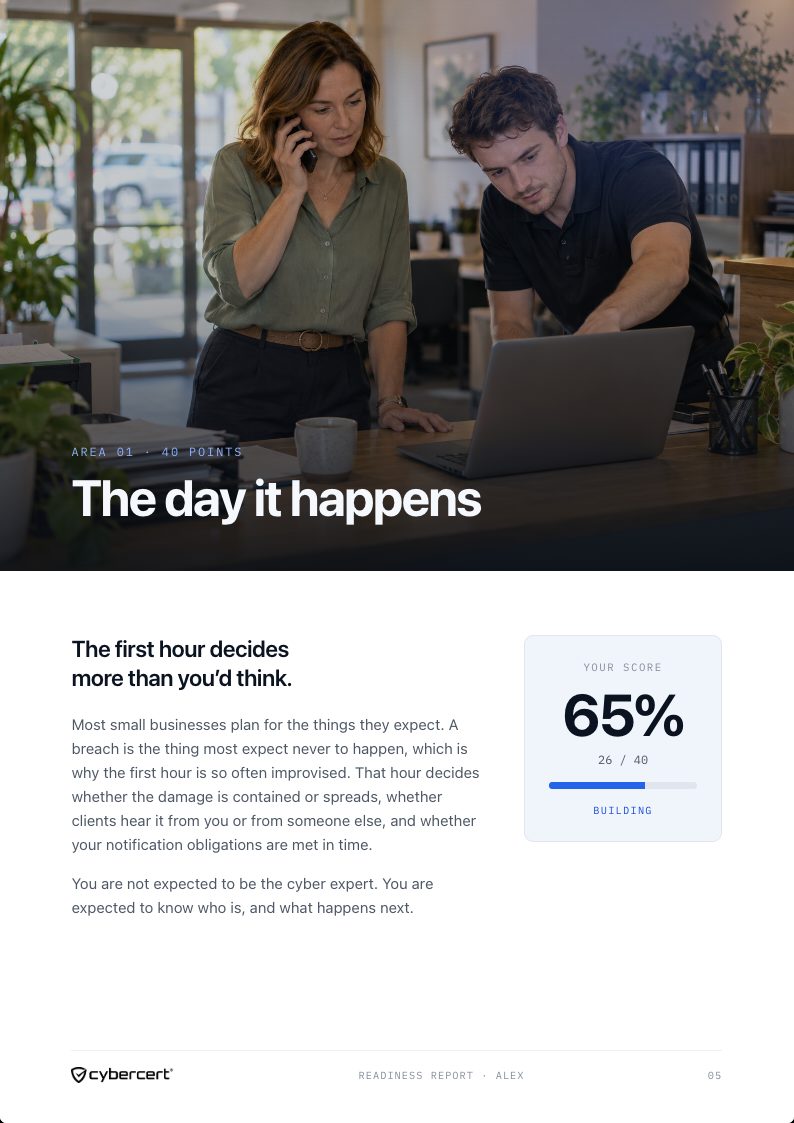
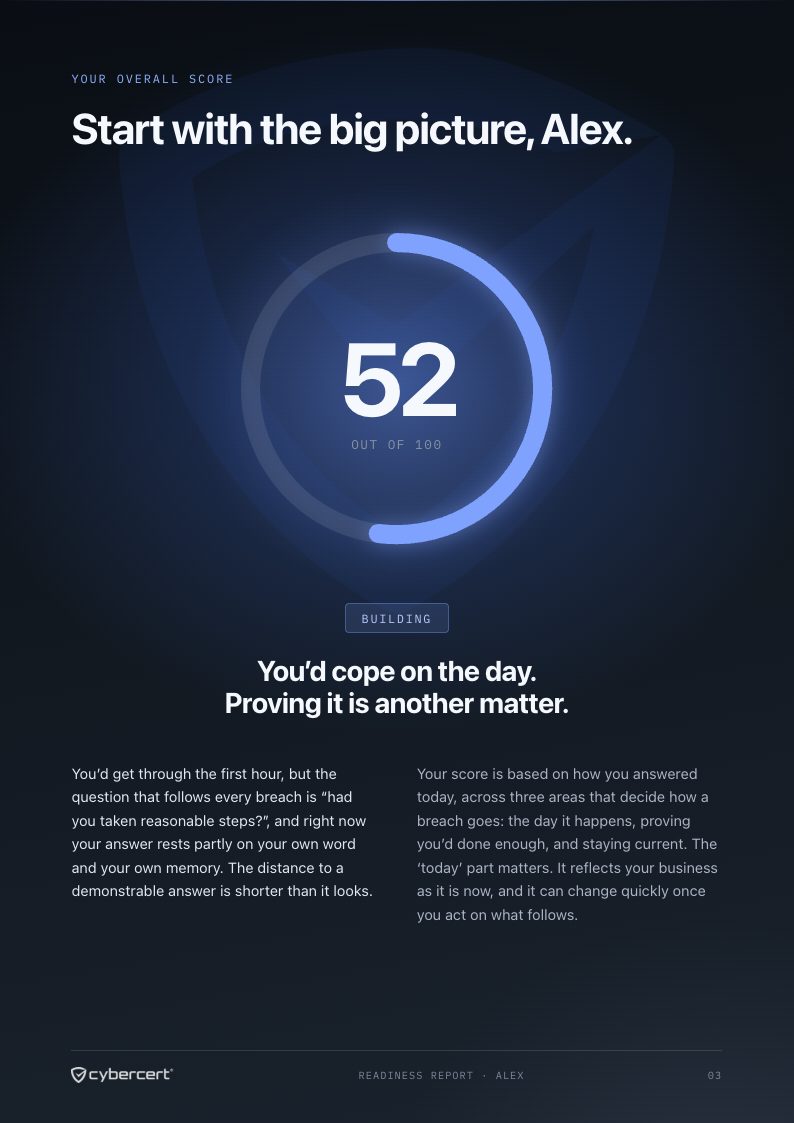
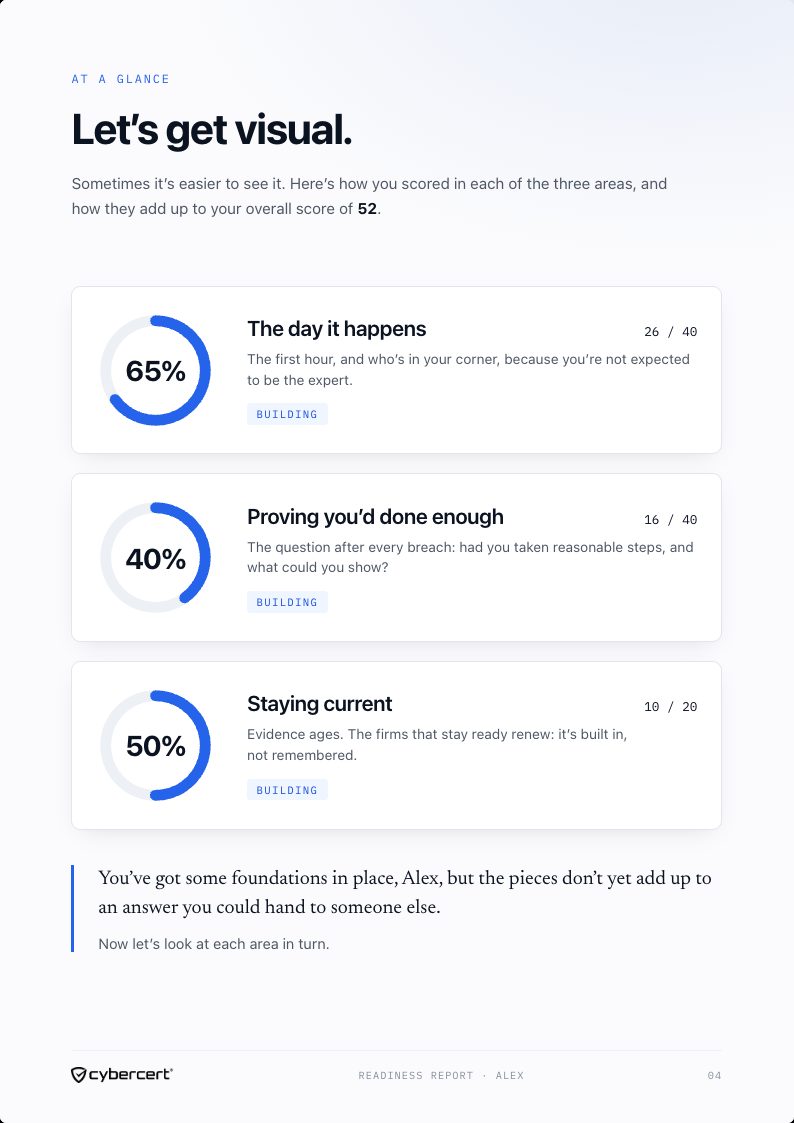
Your score across the three things that decide how it goes.
No control checklists and no audit questions. Just the day itself: what would you do, who helps you, and what could you show? We never publish or sell your answers. See our privacy policy. Your report names where you’re ready, where the day would cost you, and the plain-English reason each one matters.
Inside your report
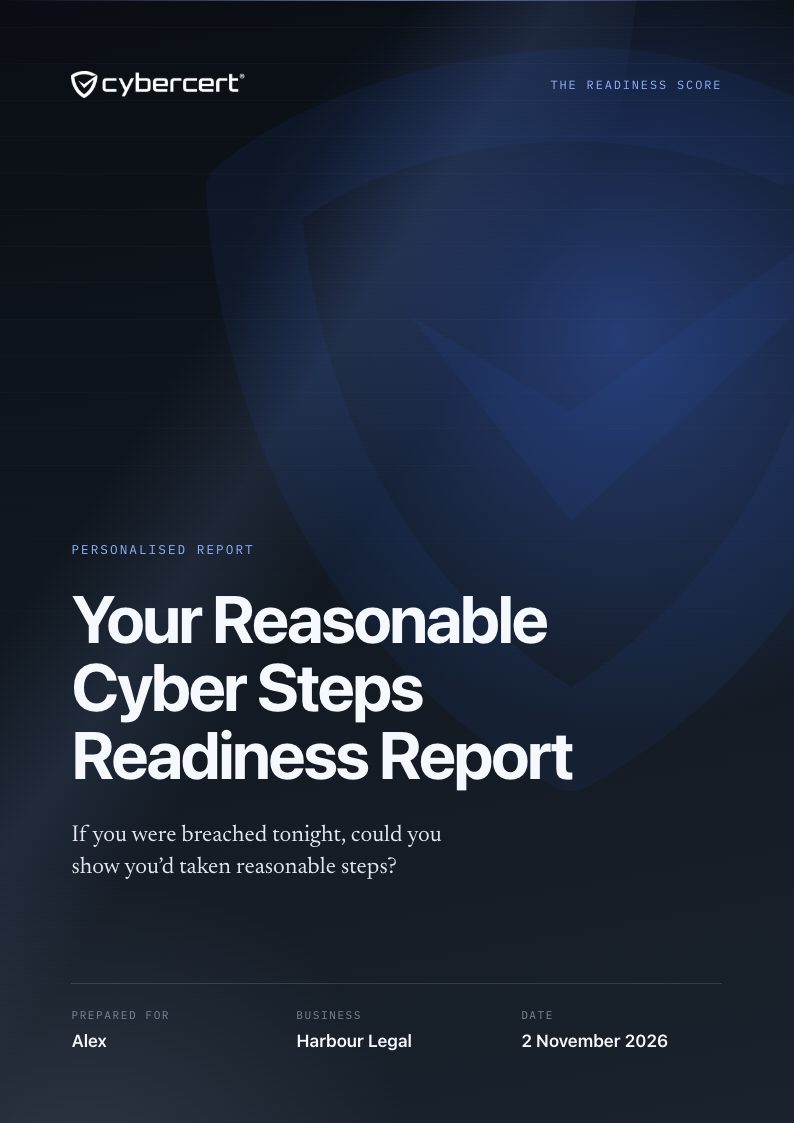
Twelve pages, written for your answers.
After your score
Not confident? That’s exactly who this is built for.
01
Take the check, free.
Three minutes. Your Reasonable Cyber Steps Readiness Report is ready to download straight away.
02
Follow the pathway built for your size.
SMB1001 meets you where you’re at and guides you step-by-step: self-paced from $95, with a certified partner beside you, or in a workshop with peers at cx.cybercert.ai/events.
03
Hold the defensible position.
Certification helps you evidence the reasonable steps you’ve taken: issued by CyberCert, an independent certification body, renewed annually and listed at verify.cybercert.ai.
The pathway
Bronze · Level 1
Small businesses with low cyber risk exposure.
$95
Silver · Level 2
Businesses requiring enhanced security.
$195
Gold · Level 3
Compliance-heavy industries.
Recommended by professional bodies
Recommended by professional bodies
$395
Platinum · Level 4
High-risk and critical sectors.
Plus independent audit
$595
Diamond · Level 5
The highest level of assurance.
Plus independent audit
$995
Proportionate to your size, guided step-by-step, independently issued and listed on a public register. Many businesses finish Silver in a sitting.
Prices plus tax if applicable.